
Unlock Anywhere® Boot-Key
Cloud QR Boot-Code
managed solution


A lost laptop is replaceable; the data on it is not. With Unlock Anywhere®, IT can block a missing Windows device's boot key from the cloud in seconds, and wipe its keys for good when it isn't coming back. No physical access needed.
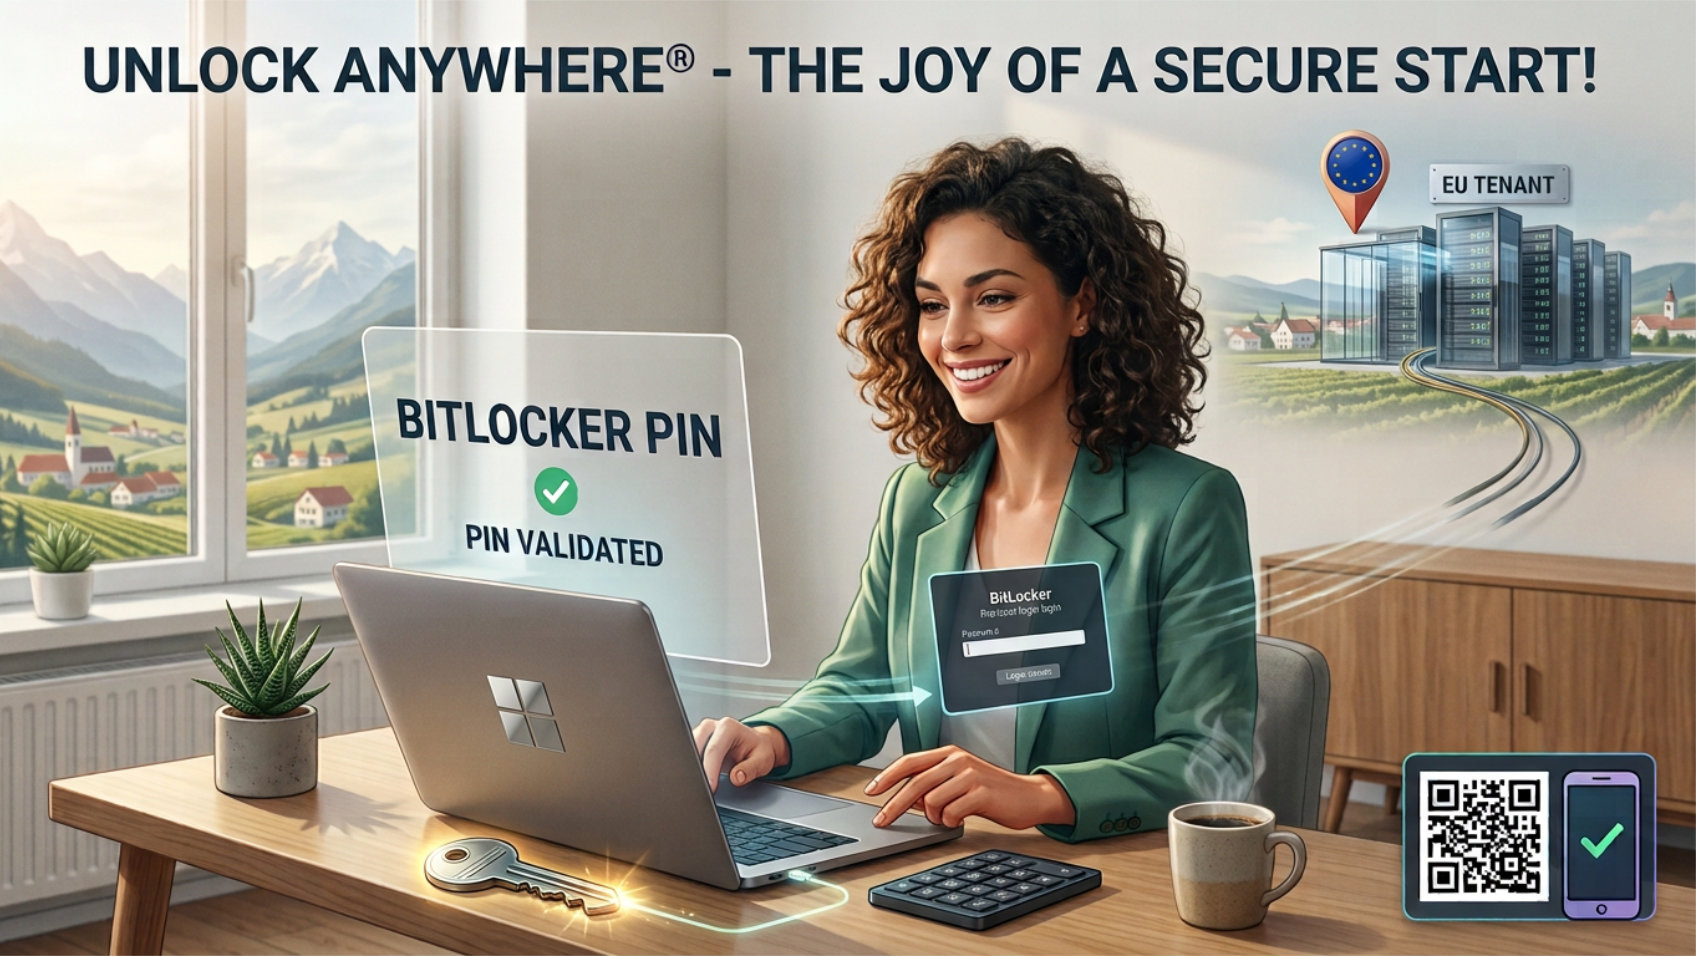
Native BitLocker PINs are checked only by the local TPM, so IT can't revoke them, see failed attempts, or help users without a recovery key. With Server-Verified PIN, Unlock Anywhere® checks the pre-boot PIN in the cloud before releasing the boot key. PINs can be revoked with one click, and every start attempt is logged. Offline devices unlock via QR code and PIN.
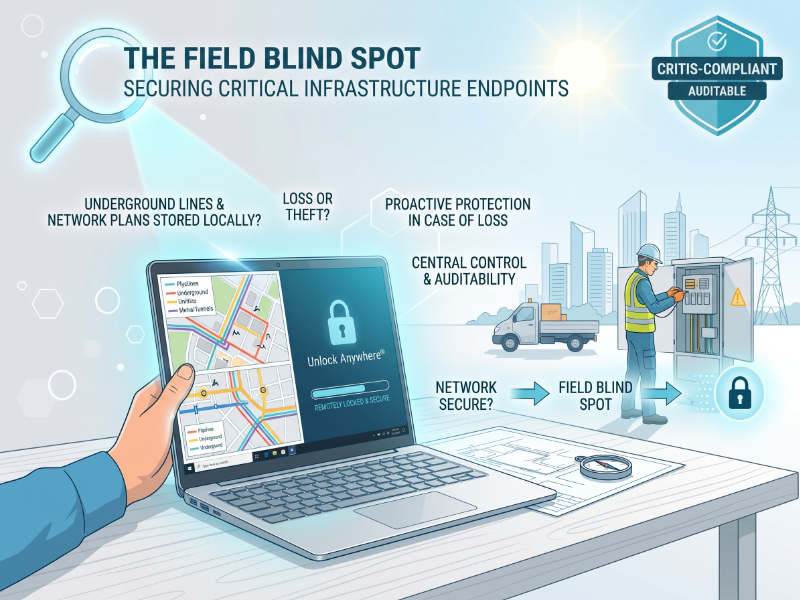
Critical infrastructure security usually focuses on SCADA systems, firewalls and data centers. Yet field technicians carry grid maps, pipeline coordinates and access credentials on their laptops every day. This article explains why a lost endpoint is both a security and a NIS2 compliance risk, and how remote lock and an auditable log help operators stay in control.
YellowKey (CVE-2026-45585) is a security feature bypass vulnerability in the Windows Recovery Environment (WinRE) that lets an attacker with brief physical access defeat BitLocker drive encryption. Using a USB drive with specially crafted FsTx files, the attacker reboots the machine into WinRE and drops into a SYSTEM-level command prompt on a volume that the TPM has already transparently decrypted — no password cracking, no special hardware, and no traces left behind. Disclosed as a zero-day in May 2026 and validated by independent researchers, it affects TPM-only BitLocker on Windows 11 and Windows Server 2025.